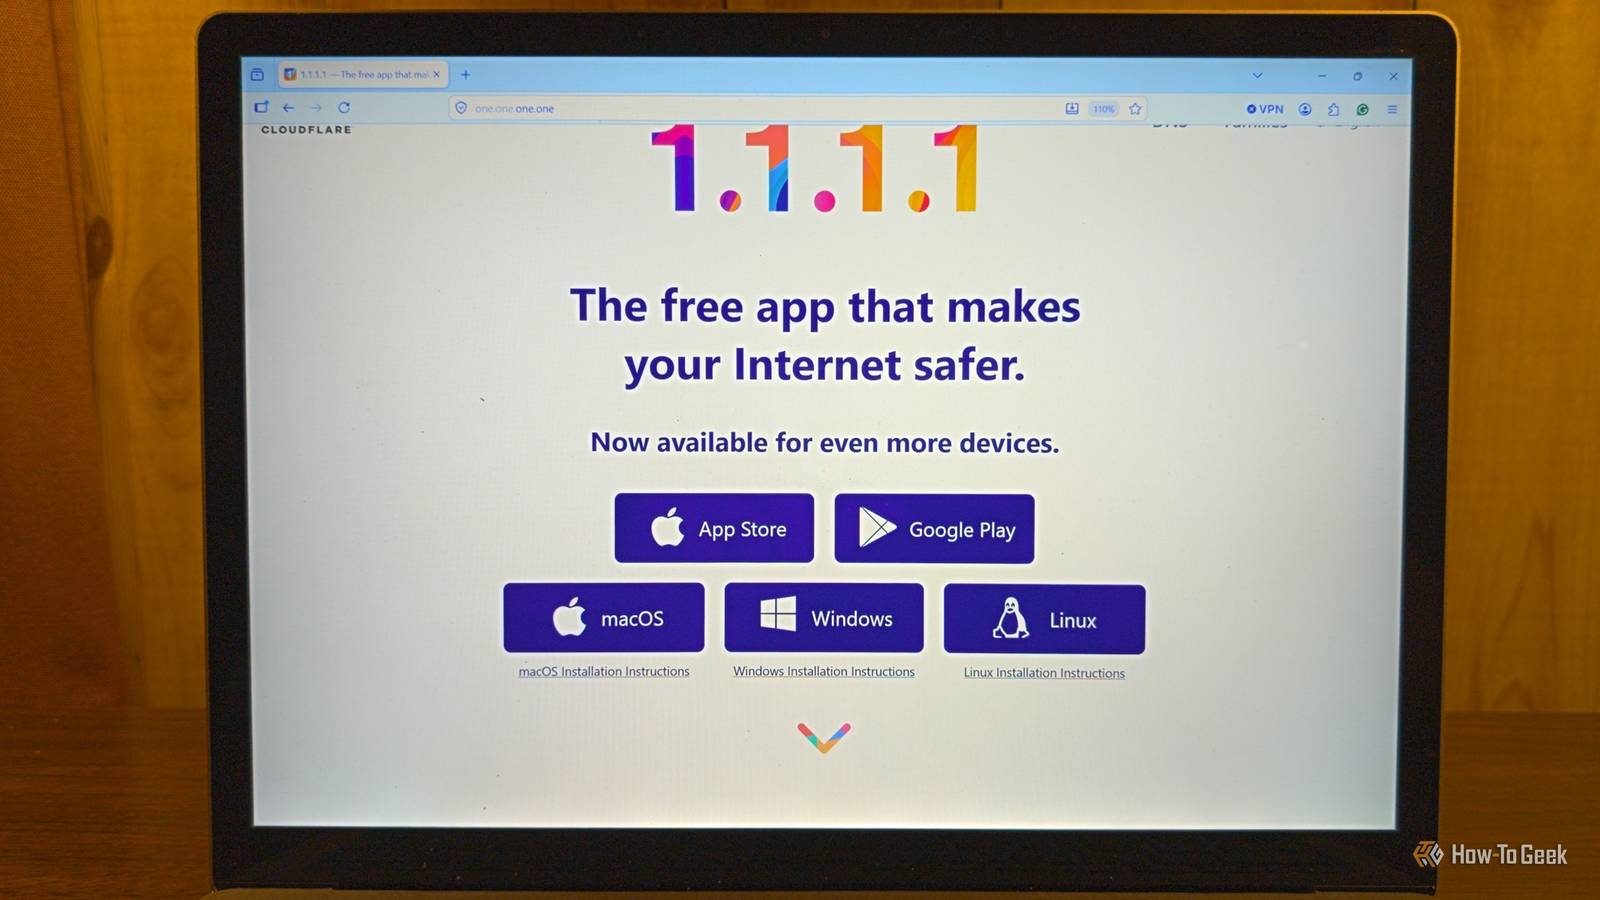
Switching your DNS server to 1.1.1.1 is common advice, and for good reason: it is reliable, fast, and theoretically, better for your privacy.Add How-To Geek on Google Add as Preferred Source Follow on Google Discover Unfortunately, changing your DNS provider only changes the service that your DNS requests, not who can see what addresses you're looking up.Despite what you might expect, standard lookup requests are transmitted unencrypted—anyone between you and the DNS server can just read them.
That also means your ISP can just see every single DNS lookup you make.If you want to hide your DNS lookups, you need to enable DNS instead.This is how you can do it.
What do DNS requests do, and why isn't changing DNS servers enough? Plain DNS is readable by anyone between you and the resolver DNS works a bit like a phone book.DNS servers allow your PC and phone to link normal, human-friendly domains like Google.com to IP addresses, which is what computers actually use when connecting to each other.Traditionally, DNS requests go out on port 53 any encryption.
It doesn't matter whether you're requesting IP addresses from CLoudflare, Google, or Quad9, that intercepts your traffic can see the details of your lookup request.In most cases, that just means your ISP.However, if you're on public Wi-Fi, whoever manages that Wi-Fi network can also see every website you connect to.
Related Your DNS server knows every website you visit—here's why Google's 8.8.8.8 is different 8.8.8.8 offers more than just a simple alternative—there are potentially privacy benefits, too.Posts 35 By Nick Lewis Though there is no such thing as perfect privacy, unencrypted DNS requests reveal far too much information about you far too easily.They can reveal what websites you use, which apps you use, and what smart devices you own.
That data may even be logged and sold to third-parties for advertising.Encrypted DNS stops some of the snooping DNS-over-TLS and DNS-over-HTTPS secure DNS requests Close Encrypted DNS addresses the DNS privacy problem by protecting your DNS lookups using the same kind of encryption that is used to secure websites.There are two common forms: DNS-over-HTTPS (DoH) and DNS-over-TLS (DoT) Both are effective, but I typically recommend DoH over DoT for one reason: resilience.
DoT can be blocked because it goes out on a specific port, 853.That makes it easy to block, and in many situations, your system will fall back to using unencrypted DNS if DoT fails.You can configure most devices to exclusively use encrypted DNS.
DoH, on the other hand, sends DNS queries alongside regular HTTPS traffic on port 443.That is the same port that web traffic travels on, which makes it much more difficult to block.As a result, I tend to opt for DoH in most cases.
When you use encrypted DNS, all your ISP sees is an encrypted connection to a DNS server.They can't see which domain you're looking up.Change your DNS settings on your router if you can One router setting covers every device You can enable encrypted DNS on a device-by-device basis, but that involves setting it up on manually.
No one wants to do that.More importantly, many devices, like smart TVs, gaming consoles, and most IoT gadgets, don't let you swap to encrypted DNS at all.However, if you enable it in your router, the entire network benefits without having to configure each device manually or worry about smart devices slipping through the cracks.
Some devices, like certain streaming sticks, have hard-coded DNS servers that bypass your router entirely.Similarly, if you use iCloud Private Relay or a browser's built-in DoH, those will bypass the router setting.To enable encrypted DNS, you need to change your router's default DNS server to a server that supports encrypted DNS and then click on the toggle that forces your router to use DoH or DoT.
Unfortunately, not all routers have that setting.If yours doesn't, you'll need to enable encrypted DNS on each device.Most routers allow you to change your DNS settings through an app.
If you want to use the router's web portal instead, just enter your router's IP address in your browser and log in.Some common router IP addresses include: 192.168.0.1 192.168.1.1 10.0.0.1 192.168.1.254 If none of those work, you can run ip route on Linux or ipconfig on Windows in the Terminal to find the address.Look for a line named "Default Gateway" or something similar.
That will be the address you need.Encrypted DNS has its limits It is important to keep an eye on what encrypted DNS do.It doesn't hide the IP address of the website you're connecting to from your ISP.
They can still easily figure out which website you're connected to by looking up that IP address on their own.If you want to hide all of that information, your only real option is a VPN.Even then, you're just changing which entity you trust with your browsing data.
Read More