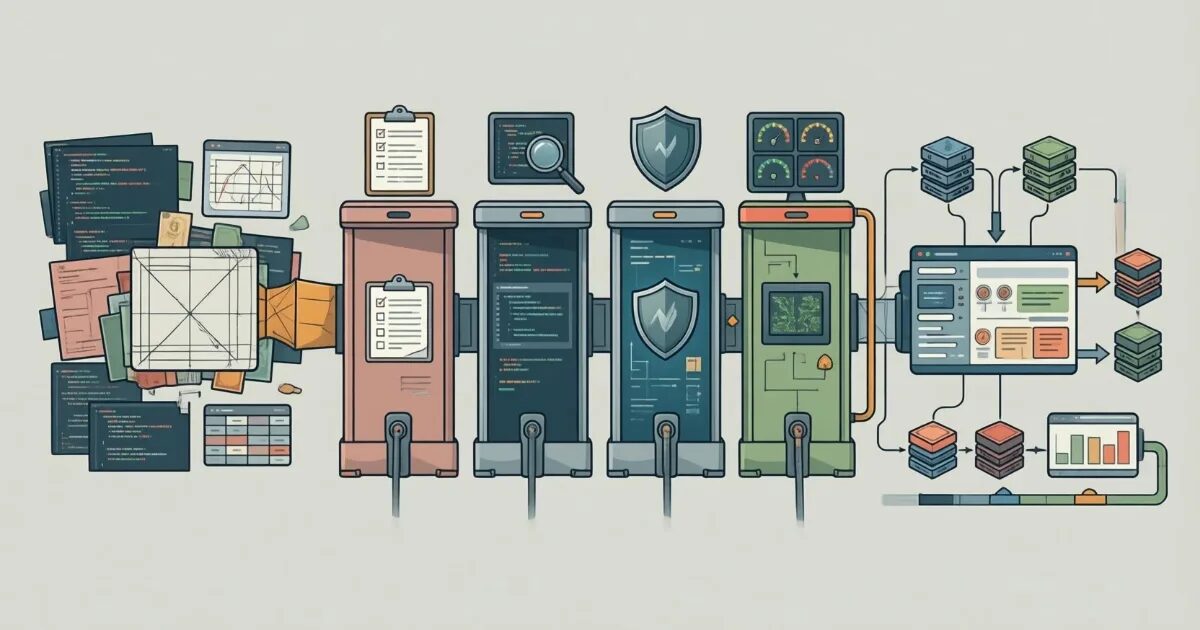
Direct answer: what makes an AI prototype ready for production?An AI prototype is ready for production when its behavior is documented, its code and access controls have been reviewed, and its data rules and deployment boundaries are tested.For data-heavy SaaS, the release decision also needs monitoring and workload tests that show how the application behaves under the tenant activity it is expected to support.Key takeawaysAudit the prototype against explicit requirements before deciding which generated code to retain.Review API contracts, data integrity and access controls as separate production requirements.Test expected tenant workloads and inspect latency, traffic, errors and saturation before release.1.Don’t Forget That Prototype and Production Solve Different ProblemsThis is why AI-assisted software development works best when AI-generated implementation is combined with human decisions about architecture, requirements, testing, and quality.
The transition requires an engineering review of the working system.ContentsDirect answer: what makes an AI prototype ready for production?Key takeaways1.Don’t Forget That Prototype and Production Solve Different Problems2.Conduct a Prototype Audit Before Refactoring3.
Establish a Source of Truth4.Convert Prototype Behavior Into Explicit Requirements5.Treat Design-to-Development Handoff as a Technical Contract6.
Build a Component System Instead of a Collection of Screens7.Evaluate Frontend Architecture Separately From Visual Quality8.Verify API Architecture and the Data Model9.
Remove Fragile Assumptions10.Establish Standards for AI-Generated Code Review11.Add UX Consistency to Production Readiness12.
Introduce Observability Before Production Deployment13.Separate Environments Before Deployment14.Perform a Security Review15.
Evaluate SaaS Architecture for the Expected ScaleConclusion: The AI Prototype-to-Production Process Is an Engineering TransitionUse the prototype to establish intended behavior; make production approval a separate engineering decision.Google’s code-review guidance puts overall design first, asking whether a change’s pieces interact sensibly and integrate with the surrounding system.Those questions apply even when the demonstrated workflow looks complete.Operational acceptance needs its own evidence.
Google’s SRE book identifies latency, traffic, errors, and saturation as four priority monitoring signals.Include them in the release discussion alongside functional behavior.This checklist addresses the application-engineering transition, including AI-assisted implementation; it does not establish the quality of any model’s outputs.
2.Conduct a Prototype Audit Before RefactoringStart the audit with a working user journey and the code that supports it.Identify which pieces implement the intended product and which exist only to make the demonstration possible.
Record unresolved decisions before assigning rewrite work.More Read Can Using Deep Learning to Write Code Help Software Developers Stand Out? Is Big Data Modeling Fighting Epidemics of Infectious Diseases? Data Analytics Contributes to the Abrupt Rise of Clean Energy Investment How a Crypto Marketing Agency Can Use AI to Create Powerful Native Advertising Strategies AI And The Acceleration Of Information Flows From Fund Managers To Investors Google’s reviewer guidance supplies two useful review lenses: system integration and complexity.It asks whether code belongs in the application or a library, and whether individual lines, functions, or classes are unnecessarily difficult to understand.Its definition of excessive complexity includes code that developers are likely to misuse or break when modifying it.Apply those questions to specific findings.
Name the affected function, its callers, and the unresolved behavior.Separate required corrections from optional cleanup.A recommendation to replace a subsystem should explain the integration or comprehension problem it addresses; “prototype code” alone is not a sufficient reason to discard it.AreaQuestions to investigateProduct behaviorWhat workflows already work, and which are incomplete?FrontendWhere are state, business logic, API calls, and rendering responsibilities located?BackendWhich services, endpoints, and integrations actually support the application?DataWhat is the source of truth for entities, relationships, and validation?InfrastructureHow are environments, credentials, deployments, logging, and monitoring configured?3.
Establish a Source of TruthFor HTTP interfaces, establish an agreed API description that both providers and consumers can consult.The OpenAPI Initiative describes its specification as a programming-language-independent way to carry API information through the lifecycle.Specifications are typically written in JSON or YAML for sharing and consumption.
Use that document as the reference for what the application exposes, and assign responsibility for updating it when the interface changes.During the prototype audit, compare the description with the implementation and record disagreements as work items.An undocumented behavior should prompt an explicit decision about whether to retain it.Keep the document’s authority bounded.
An HTTP API specification should not be treated as the complete product requirements or database design.Link those decisions to the relevant interface so reviewers can trace the intended behavior without expecting one document to answer every engineering question.4.Convert Prototype Behavior Into Explicit RequirementsWrite down what each workflow promises its consumer.
For an illustrative data-import workflow, that means deciding what constitutes an accepted submission, what happens to invalid input, and what the user can expect after completion.These are proposed requirement questions, not assumptions about the existing implementation.The OpenAPI lifecycle description places requirements work across technical and business teams, including product decisions about what an API should provide.Use that collaboration to settle behavior before developers encode conflicting interpretations.Then connect each requirement to a test at an appropriate scope.
The Practical Test Pyramid describes grouping tests by granularity and considering the number in each group.Use this as a planning framework, not a prescribed numeric ratio.Identify which checks can assess a small unit of behavior and which need cooperating parts or the complete workflow.
5.Treat Design-to-Development Handoff as a Technical ContractFor every screen that consumes data, ask the handoff to identify the information it needs and the behavior expected when that information is unavailable.Pair the visual design with the relevant API description.
Keep undecided behavior visible instead of leaving the implementing developer to infer a product decision.The OpenAPI Initiative describes OAS as a means of transferring knowledge from an API provider to its consumer.Its JSON or YAML document uses shared API terminology grounded in HTTP and JSON.This supports the interface portion of a handoff; it does not define the entire user experience.As a release practice, have design and engineering review one workflow against both artifacts.
Record any mismatch between the displayed interaction and the documented service behavior, including who must resolve it.Completion should mean that the implementation decisions are agreed, not simply that the screens have been delivered.6.Build a Component System Instead of a Collection of ScreensThe GOV.UK Design System defines components as reusable interface parts and explains that its prebuilt core elements help government teams build consistent services.
For a SaaS application, use that principle to review repeated interactions across the prototype.Inventory recurring elements and decide which should share an implementation.For a proposed data-heavy interface, candidates might include filtering controls, result summaries, and validation messages.Treat these as candidates to examine, not a mandatory component catalog.
For each shared element, document supported behavior and the differences callers may request.Review it in the screens where it will appear.Two elements that look alike may serve different tasks, so confirm their requirements before combining them.
Conversely, when several screens implement the same interaction, choose a maintained shared definition and identify the copies that should adopt it.7.Evaluate Frontend Architecture Separately From Visual QualityReview the interface in use, then inspect how its code produces that behavior.Google’s review guidance says user-facing changes particularly warrant behavioral checks because their impact can be difficult to understand from code alone.
It suggests a developer demonstration when trying the change directly is inconvenient.The same guidance asks reviewers to inspect complexity at the level of lines, functions, and classes.A visual demonstration and a code review therefore answer separate questions: whether the interaction behaves as intended, and whether maintainers can understand and modify its implementation.For a data-heavy screen, select a representative interaction and follow the code responsible for it.Ask the author to explain the path and any duplicated decisions.
Keep findings concrete, such as an unclear function responsibility or a mismatch between displayed and intended behavior.Visual polish should not close an unresolved implementation finding.8.Verify API Architecture and the Data ModelCheck the rules governing stored data alongside the API that accepts it.
PostgreSQL’s constraints documentation explains that data types can be too coarse to express application rules.A numeric type, for example, does not by itself require a positive price.Unique constraints enforce uniqueness across a column or group of columns.
For each important record, identify the rules the product actually requires and compare them with the database definition.Do not adopt an example constraint without confirming the business rule it represents.Review the HTTP interface at the same time.The OpenAPI Initiative says OAS can support service discovery, client-code generation, and API test creation.
Use the description to check whether API behavior and storage rules agree.Include tests for rejected values and duplicate submissions wherever the agreed rules make those cases relevant.9.Remove Fragile AssumptionsTurn assumptions found during the audit into named checks.
If a workflow was demonstrated only with one input shape, record what remains undecided about other inputs.If deployment settings are embedded in code, identify which values must vary across deployments.The Twelve-Factor App recommends environment variables for configuration, explaining that they can change between deployments without code changes.Apply that recommendation to deployment-specific settings, and document which values each environment requires.
Use the test-pyramid framework’s different granularities to place checks for agreed behavior.A proposed review could test a local validation rule narrowly, then check the larger workflow separately.Keep unsupported cases explicit: a successful test of the demonstrated path should not be recorded as evidence for every possible input or deployment configuration.
Close each assumption with a decision, a test, or a documented limitation.10.Establish Standards for AI-Generated Code ReviewApply a defined acceptance standard to AI-assisted changes.Ask reviewers to explain how the change fits the application, which requirement it implements, and whether its complexity is necessary.
These are proposed review requirements, not claims that generated code has a particular defect rate.Google’s code-review guidance prioritizes overall design and warns against over-engineering.It describes unnecessary generality and functionality that the system does not presently need, encouraging developers to solve the known problem.Use that standard when an AI-assisted implementation introduces extra abstractions or speculative features.Require a current requirement to justify them, or simplify the change.
A useful review record should identify the design decision and remaining concerns.Approval should reflect a human assessment of the submitted code; the method used to produce it does not answer whether it belongs in the system.DimensionReview questionsCorrectnessDoes the implementation satisfy the actual requirement?ArchitectureDoes it respect existing boundaries and responsibilities?SecurityDoes it introduce unsafe data handling or access patterns?MaintainabilityCan another developer understand and modify it?ReliabilityDoes it handle failures and unexpected states?TestabilityCan the behavior be verified automatically?11.
Add UX Consistency to Production ReadinessInspect repeated navigation across the application’s pages.W3C’s explanation of WCAG 2.2 consistent navigation states that repeated navigation mechanisms occur in the same relative order unless the user initiates a change.Its stated intent includes helping people locate information or functionality repeatedly through consistent visual layout and source order.Translate that criterion into a focused review of recurring menus and controls.
Compare their relative order across pages, and record unexpected differences.Preserve the qualification about user-initiated changes; consistency does not require preventing users from choosing a different arrangement.Keep this check separate from component reuse.Shared code is an implementation decision, while this criterion concerns the navigation users encounter.
Inspect the assembled pages, not just the component catalog.Passing this specific check should be recorded as evidence about repeated navigation, not as a declaration of complete accessibility compliance.12.Introduce Observability Before Production DeploymentChoose what the team needs to observe before approving deployment.
Google’s SRE book names latency, traffic, errors, and saturation as the four golden signals of monitoring and recommends prioritizing them when only four metrics can be measured.Teams that have run Software as a Service (SaaS) products know the routine: An alert goes off, and everyone scrambles to the observability stack first.Shahar Azulay in LLMs create a new blind spot in observability – The New StackFor this checklist, make monitoring reviewable during preproduction testing.Identify the measurements representing each signal and who will inspect them when behavior changes.Define acceptable service behavior before evaluating the results.
Collecting measurements should be followed by a practical check that the team can find and interpret them for the workflow being released.13.Separate Environments Before DeploymentDefine development, staging, and production boundaries, but avoid introducing unexamined differences in their supporting services.The Twelve-Factor App’s development-production parity guidance warns that differences between backing services can introduce incompatibilities that allow code to pass tests before failing in production.As a release practice, list the backing services used in each environment and review differences explicitly.
Where a difference remains, document what production behavior has not been exercised.Separate environments should still provide meaningful evidence about the code intended for release.The same methodology recommends storing configuration in environment variables so deployment-specific values can change without changing code.Define those values separately for each environment and check the intended configuration before deployment.
Keep service parity and configuration separation as distinct decisions: matching service choices does not require pointing every environment at the same running resource.14.Perform a Security ReviewExamine every API operation that accepts an object identifier.OWASP’s 2023 API Security Top 10 says object-level authorization checks should be considered in every function accessing a data source through an ID supplied by the user.
For SaaS, propose tests that attempt access to records outside the caller’s permitted scope.Review resource consumption separately.OWASP identifies network bandwidth, CPU, memory, storage, and paid API integrations as resources consumed by requests.It warns that attacks can cause denial of service or increased operational costs.Map the application’s resource-consuming operations and decide which require enforceable limits.
Treat those limits as proposed controls whose adequacy must be tested, not as automatic protection.Record authorization and resource-consumption findings independently: permission to access an object does not settle how much work a request should be allowed to trigger.15.Evaluate SaaS Architecture for the Expected ScaleDescribe expected scale in terms of both tenants and users.
Microsoft’s multitenancy guidance defines a multitenant solution as one used by multiple customers and distinguishes tenants from individual users.Multiple users belonging to one organization or group can form a single tenant.Build proposed workload scenarios around that distinction.State the assumed tenant count, users per tenant, and operations being exercised.
For a data-heavy application, include the data quantities relevant to those scenarios.Label these values as planning assumptions until measurements or actual usage support them.Assess each scenario using Google’s four monitoring signals: latency, traffic, errors, and saturation.Report the workload alongside the results.
A release decision should specify the operating conditions tested and the unresolved limits, without turning a successful test at one workload into an unrestricted scalability claim.Conclusion: The AI Prototype-to-Production Process Is an Engineering TransitionBegin with an audit of one complete workflow, from its interface and API contract to its stored data and deployment configuration.Record each unresolved requirement, review finding, and missing test with an owner.Then assess the expected tenant workload using the monitoring signals defined for release.
Use that evidence to decide what can ship, what needs correction, and which operating limits must remain explicit.Expand the audit until it covers the intended production scope.
Read More